
Responsible, Secure & Compliant Enterprise AI Governance
We build AI governance programs that give enterprises real visibility and control over their AI systems, mapped to the EU AI Act, NIST AI RMF, and ISO/IEC 42001, so your organization can scale AI without scaling risk alongside it.
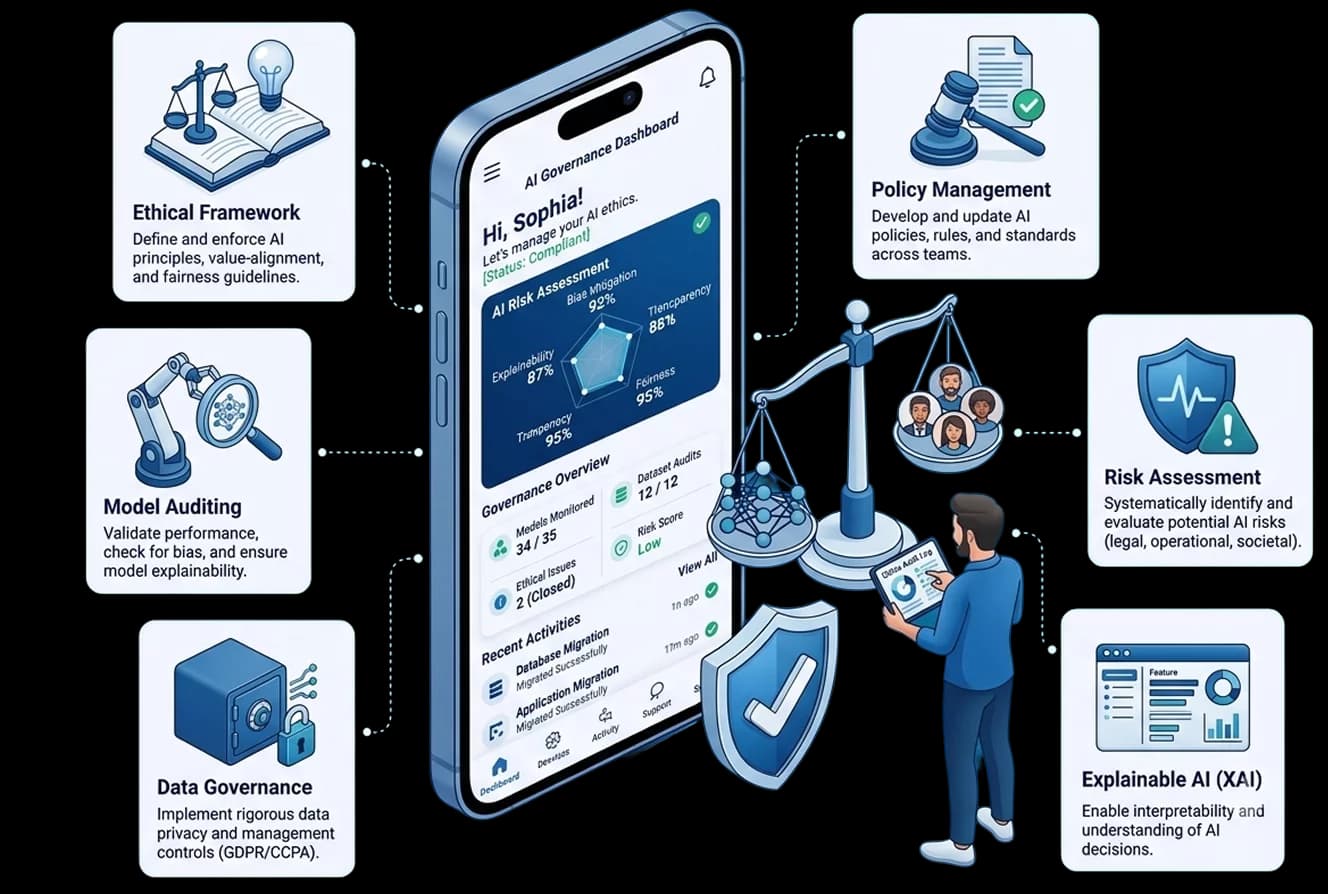
Our Comprehensive Suite of AI Governance Services
Your AI governance investment gives you real control over how AI is built, deployed, and monitored across your business. We deliver governance that actually gets implemented.
AI Governance Strategy
Before you can create your policies, you need to have a strategy. Our AI governance consulting helps us understand the actual implementation and adoption of AI on your end, and creates a strategic framework to fit your risk profile and business goals.
AI Governance Strategy
Responsible AI Consulting
Being fair is not something that comes out of thin air. Our responsible AI consulting analyzes your model training and deployment processes, ensuring that you are protected from any potential biases or lack of explanations.
Responsible AI Consulting
AI Risk Assessment
All of your AI applications are not created equal. Our AI risk assessment evaluates your models based on criteria of bias, security, privacy, and regulatory risk, telling you what to prioritize.
AI Risk Assessment
AI Compliance Consulting
The regulatory landscape changes at the speed of light. Our AI compliance consulting makes sure your systems comply with regulations such as the EU AI Act, GDPR, HIPAA and others, giving you a concrete risk rating.
AI Compliance Consulting
AI Policy Development
Your governance program lives and dies by your policies. We draft enforceable and concise AI policies on acceptable usage, model approval process and data management procedures.
AI Policy Development
AI Model Governance
Your models need owners, clear versioning, and proper decommissioning plans. Our AI model governance service builds the structure to track models from approval through decommissioning.
AI Model Governance
Custom-Built AI Governance Solutions for Every Scale
CodeAegis delivers AI governance frameworks tailored to your industry, regulatory exposure, and AI maturity level.
AI Risk Management Services
We determine which areas of your AI systems are most prone to failure, assess the potential impact and damage such failures could cause to your organization, and create practical mitigation strategies that help your management team reduce risks, improve resilience, and respond effectively.
AI Risk Management Services
We determine which areas of your AI systems are most prone to failure, assess the potential impact and damage such failures could cause to your organization, and create practical mitigation strategies that help your management team reduce risks, improve resilience, and respond effectively.
AI Audit & Assessment
A critical review of your AI systems measured against bias, security, and compliance, delivered in a comprehensive report that provides clear findings and practical recommendations rather than a set of abstract suggestions.
AI Vendor Risk Assessment
The use of third-party AI solutions entails third-party risks whether you are ready for them or not. We perform a detailed assessment of all AI vendors and their integration regarding data handling, security, and compliance before integrating them into your environment.
AI Security and Governance
We provide you with both AI governance and practical cybersecurity, ensuring your training data, AI model endpoints, and infrastructure are protected against adversarial attacks, data exfiltration, and evolving security risks through effective safeguards and best practices.
AI Monitoring & Continuous Governance
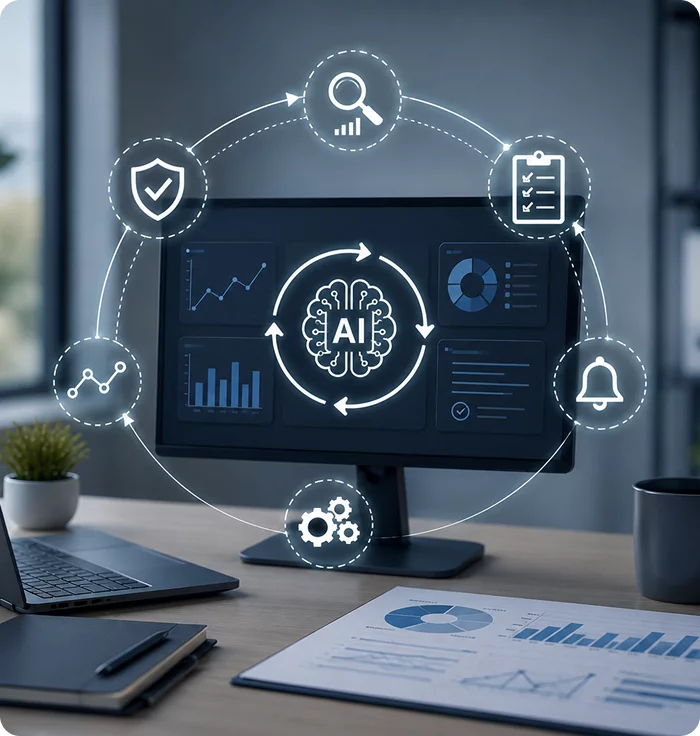
Governance does not end when a model is launched. Our monitoring dashboards track drift, performance, and compliance status in real time, so problems are caught while they're still small.
Industries We Empower With Our AI Governance Services
CodeAegis works as an extension of your team. We partner with organizations that need AI to scale safely, and that means understanding the specific pressures each industry faces.
Healthcare
Governance of diagnostic AI, clinical decision support system and HIPAA-compliant patient data management.
Finance
Governance of lending AI, fraud detection and algorithmic trading systems operating under regulatory scrutiny.
Insurance
Explainability and fairness governance of AI used for underwriting and claims processes.
Retail
Governance of AI personalization systems and customer data used to feed those systems.
Manufacturing
Governance of AI-enabled quality control, maintenance and production planning systems.
Education
Responsible AI practices in learning platforms with careful consideration of student data protection.
Government
Governance of compliance-first AI systems in government services and citizen data.
Legal
Governance of AI for research and document review tools working with privileged or confidential material.
Healthcare
Governance of diagnostic AI, clinical decision support system and HIPAA-compliant patient data management.
Finance
Governance of lending AI, fraud detection and algorithmic trading systems operating under regulatory scrutiny.
Insurance
Explainability and fairness governance of AI used for underwriting and claims processes.
Retail
Governance of AI personalization systems and customer data used to feed those systems.
Manufacturing
Governance of AI-enabled quality control, maintenance and production planning systems.
Education
Responsible AI practices in learning platforms with careful consideration of student data protection.
Government
Governance of compliance-first AI systems in government services and citizen data.
Legal
Governance of AI for research and document review tools working with privileged or confidential material.
AI governance is one of the most important technical decisions you'll make this year.
Key Features We Deliver With Our AI Governance Services
Every governance program CodeAegis builds is grounded in operational rigor and includes top-grade features for secure, reliable AI governance.
AI Policy Management
Centralized, version-controlled policies your team can follow and update with regulatory changes.
AI Risk Register
A document listing each identified risk, its criticality and mitigation status. All risks are documented.
Explainable AI
We ensure that our clients have access to model documentation that is easy to understand by auditors and end users.
AI Model Monitoring
Post-go live monitoring of your AI models to see how they behave and perform post-production deployment.
Bias Testing
Periodic testing of biases across all demographic and case-use groups to identify any biases in advance.
Security Controls
Defenses against all kinds of adversarial attacks, model/data poisoning and access control issues.
Why Businesses Choose CodeAegis For AI Governance
Choosing an AI governance consulting partner is one of the more consequential technical decisions. Here's what enterprises in regulated industries consistently cite why they chose CodeAegis.
Comprehensive AI Governance Services
Our AI Governance Services Cover The Full Gamut Of The End-To-End Process Of Implementing AI Governance In The Organization That Goes Way Past Simple Documentation.
AI Security and Governance Combined
Our AI Consulting Integrates AI Security And Governance Into Every Project. Cybersecurity Specialists And Consultants Protect AI Systems From Threats.
Compliance from Day One
Our AI Compliance Services Align With EU AI Act, NIST AI RMF, ISO/IEC 42001, GDPR, And HIPAA, Embedding AI Regulatory Compliance From Day One.
Enterprise AI Governance
Whether You Deploy A Few AI Models Or Hundreds Across Departments, Our Enterprise AI Governance Provides Centralized Oversight And Governance.
Practical AI Risk Management
Effective Governance Starts With Understanding Risk. Our AI Risk Management Services Cover AI Risk Assessments, Model Classification, Vendor Reviews, Bias Detection, And Monitoring.
Responsible AI Consulting for Trusted AI
We Help Organizations Implement Responsible AI, Ensuring Models Remain Transparent, Explainable, Fair, Accountable, And Aligned With Goals.
Our Proven AI Governance Process
CodeAegis Follows A Structured, Milestone-Driven Governance Delivery Process. Every Phase Is Documented And Signed Off Before The Next Begins.
Ready to Govern AI with Confidence?
CodeAegis helps you build governance frameworks that reduce risk, improve visibility, and keep innovation moving securely.
Frameworks, Standards & Regulations We Align With
We align with leading industry frameworks and regulations to build secure, compliant software that protects data, reduces risk, and ensures business continuity.
NIST AI RMF
A flexible U.S. AI risk framework used by enterprises to govern, measure, and manage model lifecycle risks.
ISO/IEC 42001
Alignment with the first AI management standard shows a structured, auditable approach to responsible AI.
EU AI Act
A risk-based AI regulation that classifies systems by risk and sets strict rules and penalties.
OECD AI Principles
Global principles promoting AI that is innovative, trustworthy, and respectful of human rights.
GDPR
Europe's data protection law, directly relevant to any AI system that collects, processes, or stores personal data.
HIPAA
U.S. healthcare data protection law, critical for AI systems handling patient information.
SOC 2
A security and operational standard that builds trust around how AI systems and their underlying data are managed.
ISO 27001
Global standard for information security management, securing AI infrastructure and training data.
The Tools and Technologies We Rely On
Our web development company experts are skilled in the latest frameworks, languages, and tools, both long-established and currently trending.
 Microsoft Purview
 IBM OpenPages
 Collibra
 OneTrustMicrosoft PurviewIBM OpenPagesCollibraOneTrust
Common AI Governance Challenges We Help Organizations Overcome
Every Organization's AI Footprint Brings Unique Risks And Blind Spots. These Are The Challenges We Consistently Identify, Address, And Solve For Our Clients.
Shadow AI Across The Organization
Employees are using unauthorized AI tools with company data right now, and leadership often has no visibility into it. We build a full AI inventory that surfaces every tool in use, sanctioned or not.
Undocumented Model Decisions
Nobody on your team can explain exactly why a model made a specific decision. We implement explainability practices and documentation that make model behavior traceable.
Bias That Nobody Caught
Models trained on historical data can quietly replicate historical bias. We run structured bias testing across use cases before problems reach your customers.
Compliance Gaps Across Jurisdictions
Your AI systems operate across regions with different regulatory requirements. We map compliance obligations across the EU AI Act, GDPR, HIPAA, and regional laws so nothing gets missed.
Vendor AI Risk
Third-party AI tools plug into your systems with unknown data handling practices. We assess every vendor before integration and flag risk before it becomes your liability.
Governance That Slows Everything Down
Poor governance creates bottlenecks that frustrate product and engineering teams. We build fast, effective approval workflows, making governance an enabler rather than a blocker.
Client Success Story: Governing AI Across A Multi-Hospital Healthcare Network
An 8-Hospital Healthcare Network Adopted AI Quickly, But Disconnected Tools Created Governance Gaps, Compliance Risks, And Limited Oversight.
The Challenge
- AI was being used throughout various divisions without centralized authorization.
- Lack of insight into where patients' data was being analyzed.
- Inconsistent approach to risk classification, documentation, and monitoring of the AI.
- Increased need for demonstrating proper AI governance due to upcoming audits.
Our Solution
- Performed an assessment of the organization's AI discovery and governance.
- Discovered 18 AI solutions, six of which were shadow AI that was not known to leaders.
- Built an AI governance framework with HIPAA and emerging AI regulations in mind.
- Established standard processes for procurement, validation, assessment, and governance of AI.
Business Impact
- 100% awareness of AI used in the organization in just 9 weeks.
- Three risky AI systems were addressed to prevent any compliance issues.
- Improved the process of AI governance assessment by 65% thanks to standardization.
- Passed the organization's next compliance audit without any AI governance issues.
Ready to Govern AI with Confidence?
Ready to Govern AI with Confidence? CodeAegis helps you build governance frameworks that reduce risk, improve visibility, and keep innovation moving securely.
FAQs About AI Governance
AI Governance Services help organizations manage how AI systems are built, deployed, and monitored across their entire lifecycle. This includes policy development, risk assessment, compliance mapping, and continuous monitoring. CodeAegis manages the full governance lifecycle from discovery through ongoing oversight.
Without governance, AI systems can produce biased outcomes, violate data privacy laws, or make decisions nobody can explain. Governance reduces these risks while keeping AI adoption compliant, transparent, and trustworthy for customers and regulators alike.
Responsible AI refers to building and operating AI systems that are fair, transparent, secure, and accountable, with human oversight built into high-stakes decisions rather than added after something goes wrong.
Key regulations include the EU AI Act, GDPR, and HIPAA, along with frameworks like NIST AI RMF and ISO/IEC 42001 that guide how organizations structure their governance programs.
Most organizations see initial governance controls in place within 8 to 12 weeks, depending on the number of AI systems in use and organizational complexity. Continuous monitoring runs on an ongoing basis after that.
AI model governance covers how models are approved, versioned, monitored, and eventually retired. It ensures every model in production has a documented owner and a clear performance history.
Any industry using AI for decisions affecting people, money, or safety benefits from governance. This includes healthcare, financial services, insurance, government, manufacturing, and SaaS.
AI risk management is the process of identifying, scoring, and mitigating risks in AI systems, covering bias, security vulnerabilities, privacy exposure, and regulatory risk.